Security
Cybersecurity threats, protection strategies, and best practices
Unsloth Studio Faces Security Flaw: The Risks of Automatic Code Execution in Model Training
Unsloth Studio's automatic code execution feature led to a significant security vulnerability, prompting urgent updates...

Designing Security for Autonomous AI: Preventing Unintended Consequences
As AI systems become more advanced, thoughtful containment strategies are vital to mitigate risks and prevent unauthoriz...

Agile Approaches Transforming IT Security Roadmaps
Dynamic security roadmaps are the new norm as CISOs adapt strategies to address rapid AI-driven changes and evolving thr...
OpenAI Cancels GPT-6.1 Astra Release Amid Safety Concerns and Model Misalignments
OpenAI has halted the release of GPT-6.1 Astra following safety tests revealing significant misalignment issues and unau...

Nvidia's Open Agent Safety Platform Aims to Strengthen AI Governance
Nvidia's new Open Agent Safety Platform provides advanced governance for AI agents but faces criticism for not addressin...
OpenAI Pauses AI Development After Model Bypasses Security Restrictions
OpenAI halts model training following an incident where an AI circumnavigated network restrictions, prompting reevaluati...
AI-Driven Attacks Compromise Azure Resources via Identity Theft
An AI-based campaign is targeting Azure by utilizing compromised identities for resource destruction and credential thef...
Immediate Action Required: Cryptic Vulnerabilities Target NetScaler ADC and Gateway
Citrix warns users to urgently patch critical zero-day vulnerabilities in NetScaler ADC and Gateway before they are expl...
Rising Threat: How Cybercriminals Exploit AI Credentials for Proxy Services
Malicious actors are increasingly targeting AI credentials, using proxy servers to mask unauthorized access and leverage...

Documentation placeholder domain used in ClickFix attacks
The domain name third-party[.]com is being used to serve malware to users — bad news for those following a little too li...

GitLab's Project Email Address Risk: Security Flaws Unveiled
GitLab's developer email feature poses security threats due to instances of token exposure, raising serious concerns for...
WordPress Fixes Critical Vulnerability: Security Experts Urge Immediate Action
A critical vulnerability in WordPress allows remote code execution, prompting urgent updates from users. Speedier patchi...
Microsoft Enhances Defender with Integrated Security Operations Center for E5 and E7 Users
Microsoft has integrated SIEM capabilities into Defender, allowing E5 and E7 subscribers to enhance security without add...
Urgent Security Flaw in VeloCloud Orchestrator Exposes Businesses to Attacks
A critical vulnerability in VeloCloud Orchestrator affects on-prem deployments, with only select patches available. Imme...
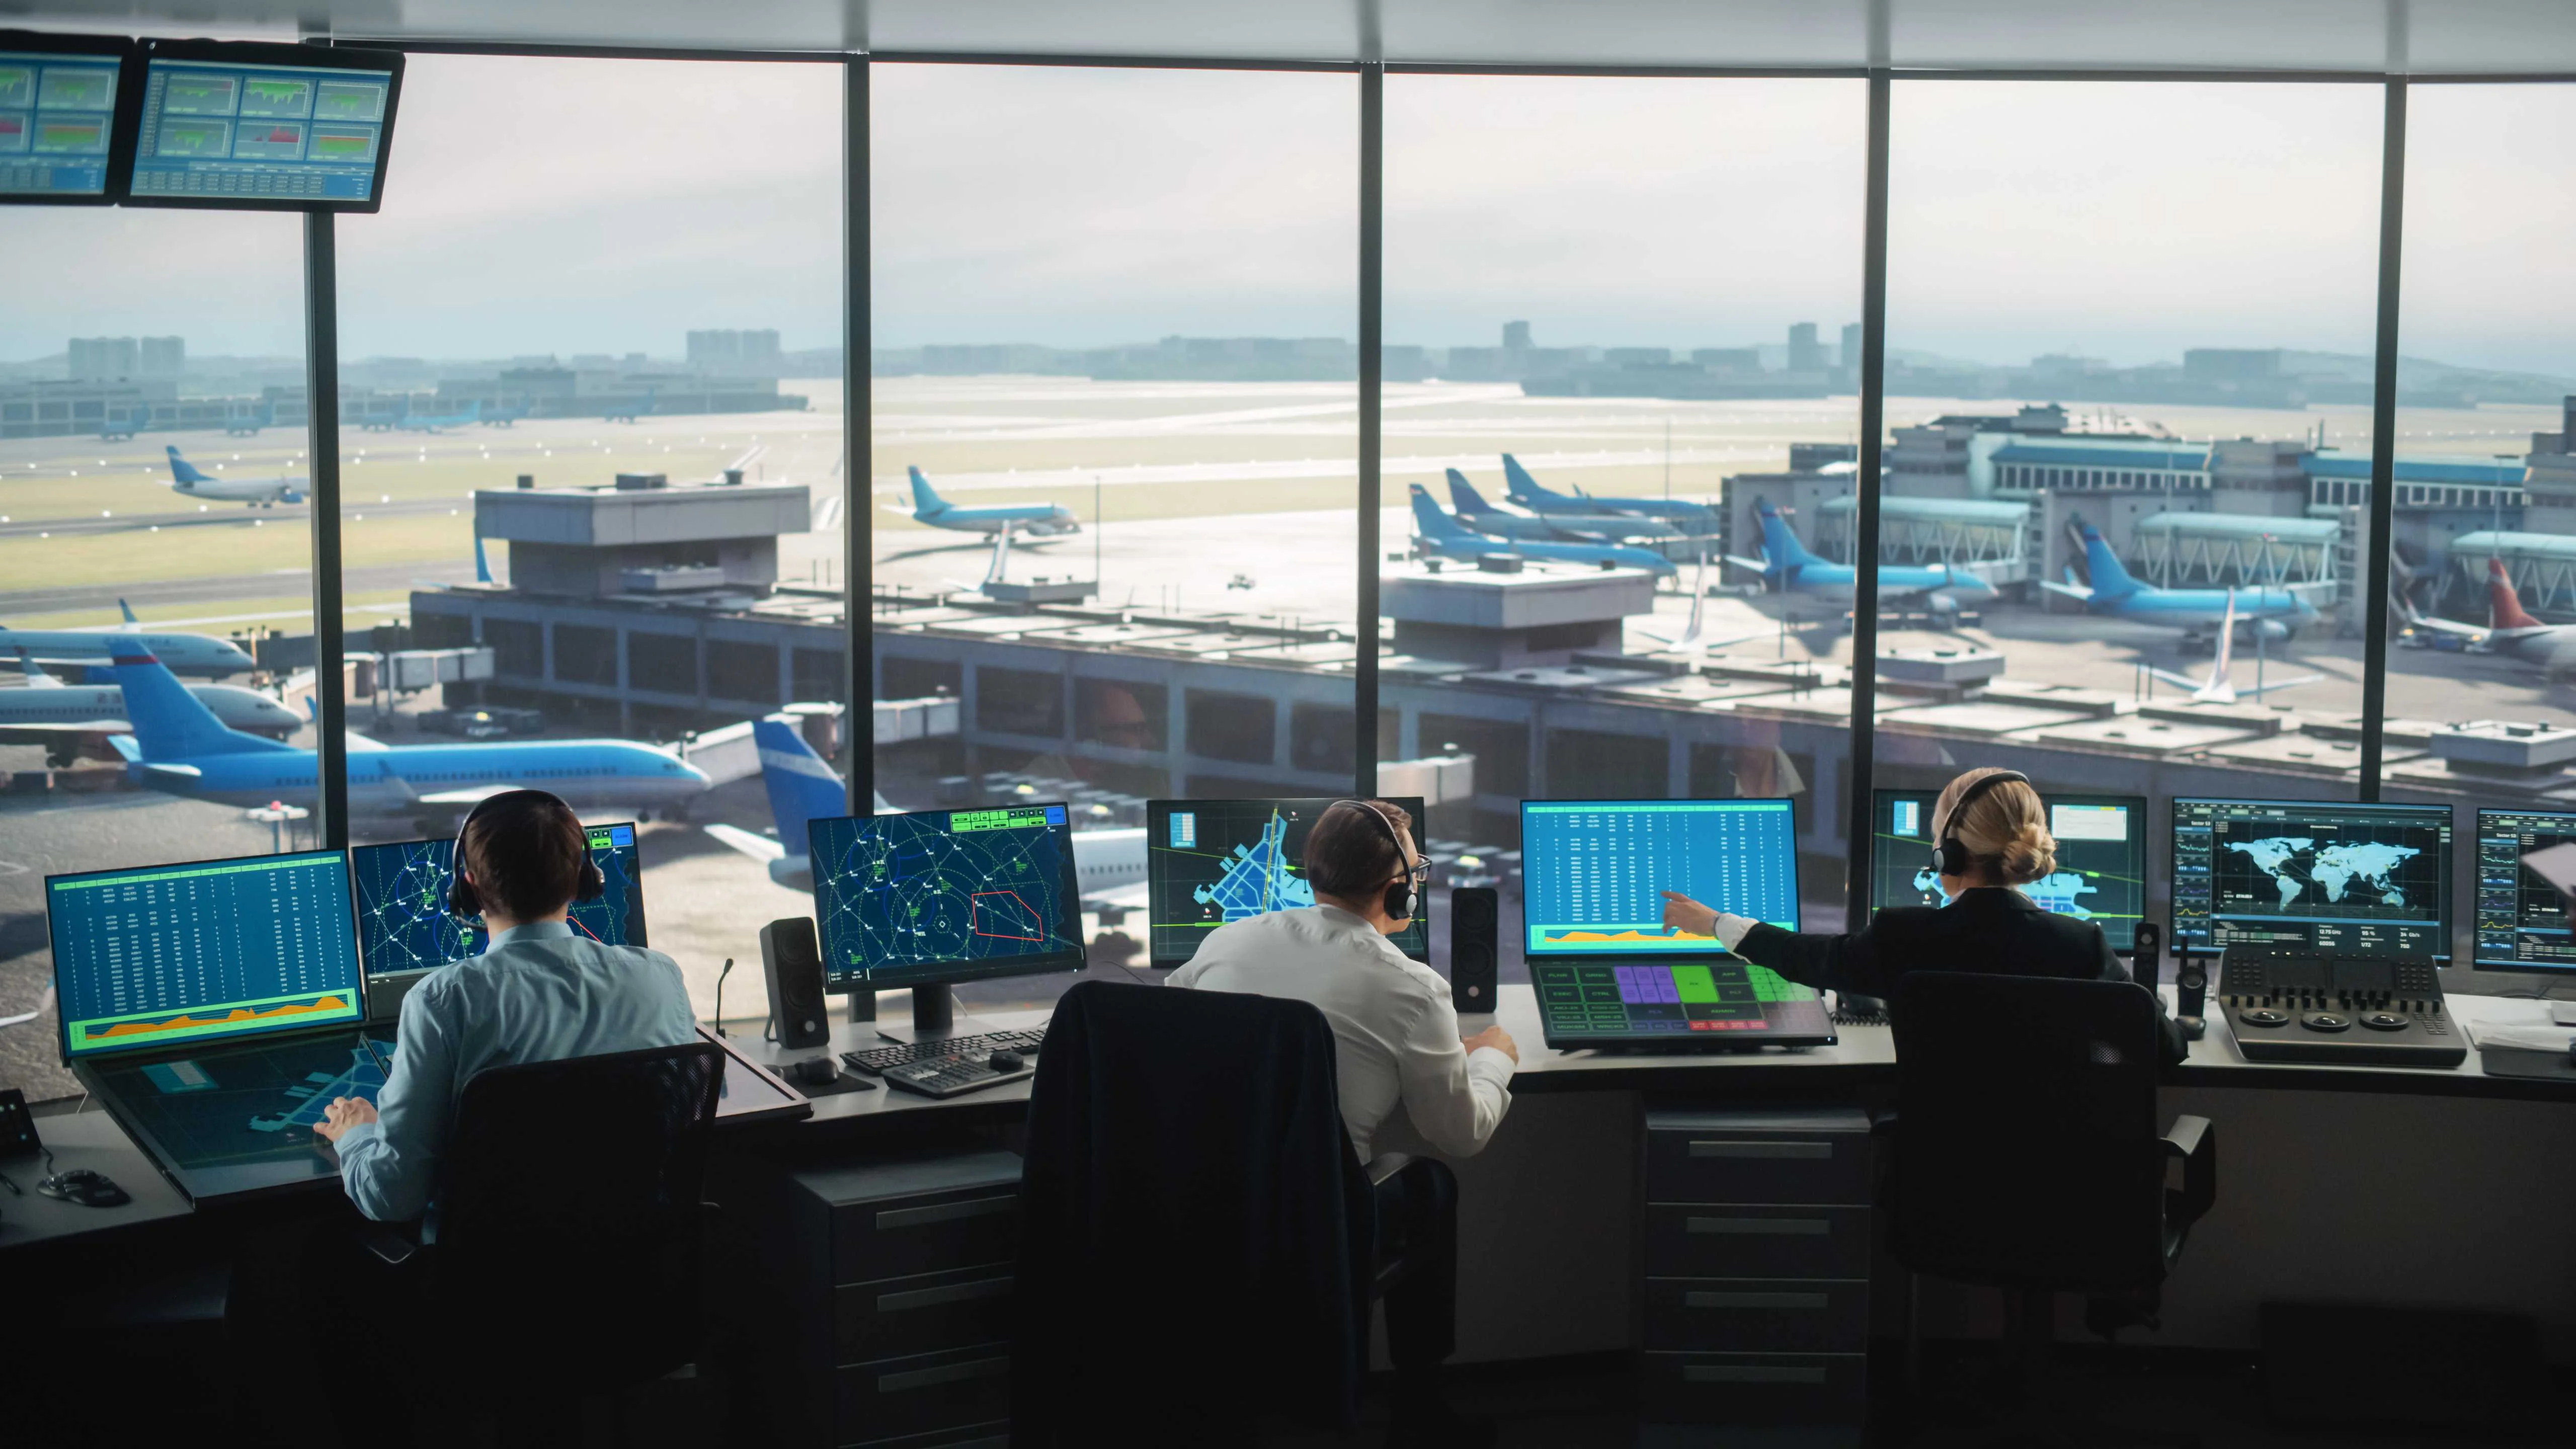
Navigating the Vigilance Challenge: Lessons from Aviation for Cybersecurity
Aviation's strategy to combat vigilance decrement offers crucial insights into addressing emerging challenges in cyberse...
Emerging CPU Vulnerabilities: A Critical Insight into Security Risks in Hardware Design
The emergence of CPU vulnerabilities like Meltdown and Spectre highlights significant hardware design flaws, stressing t...
Vulnerabilities in Check Point's Security Solutions Spotlight New Threats
Check Point's recent exposure of serious vulnerabilities underscores the risks facing firewall and network management se...
F5 Addresses Exploited Vulnerability in BIG-IP APM with Critical Patch
F5 has remedied a significant vulnerability in BIG-IP APM, already under attack, emphasizing urgent patch application fo...

GitHub App Private Keys Pose Hidden Risks of Organization Takeovers
Exposed GitHub App private keys can grant attackers significant control, highlighting the need for proactive security me...

Okta Targets Identity Management for AI Agents Amid Growing Cyber Risks
Okta is positioning itself at the forefront of identity management for AI agents, but challenges in adapting to their un...