Analytics
Data analysis, big data, and business intelligence

OpenAI built an AI pipeline to find, exploit and patch Linux flaws
OpenAI has developed an autonomous AI pipeline that can identify software vulnerabilities, develop working exploits to v...

OpenAI’s GPT-6 Cyber ups the ante on vulnerability discovery
OpenAI is introducing GPT-6 Cyber, a restricted access model that the company calls its most capable and aligned cyberse...

Debian, Ubuntu patch APT flaw that could hand attackers root
Linux administrators’ trust in package managers is being tested by a newly disclosed vulnerability in APT, the package m...
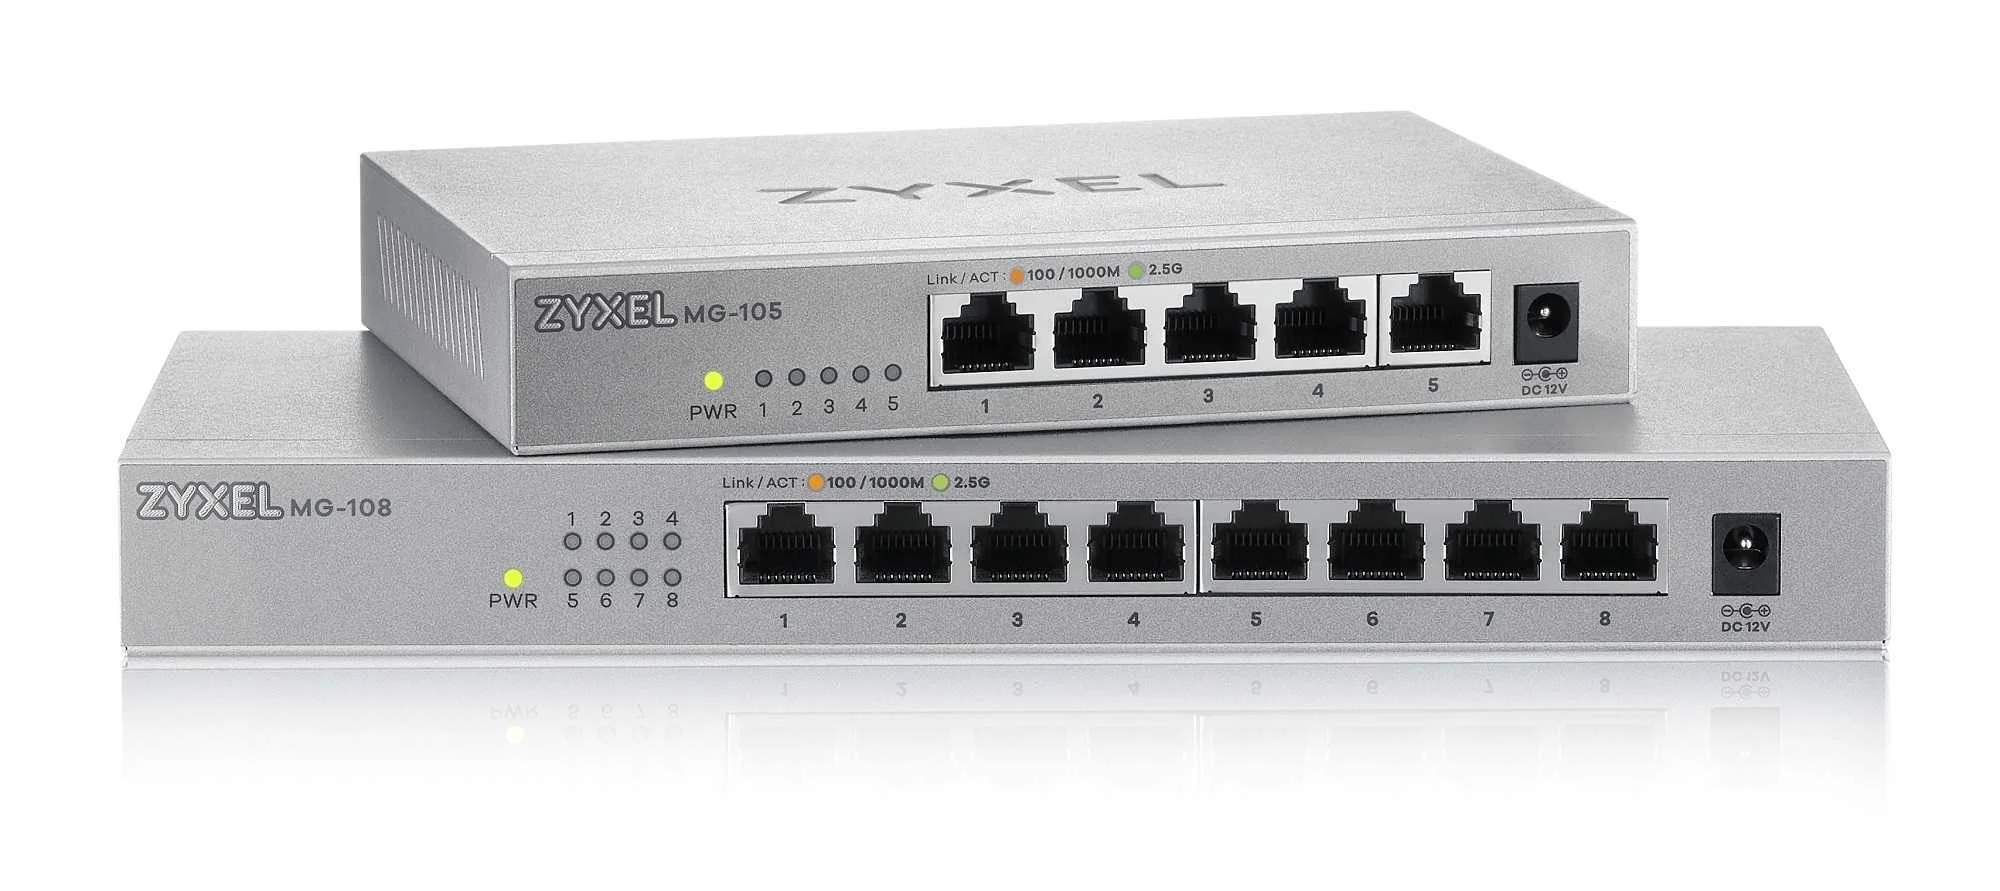
Zyxel patches a zero-day hiding behind an old fix
Zyxel has patched a zero-day vulnerability that attackers exploited to compromise 996 GS1900 network switches across 48...
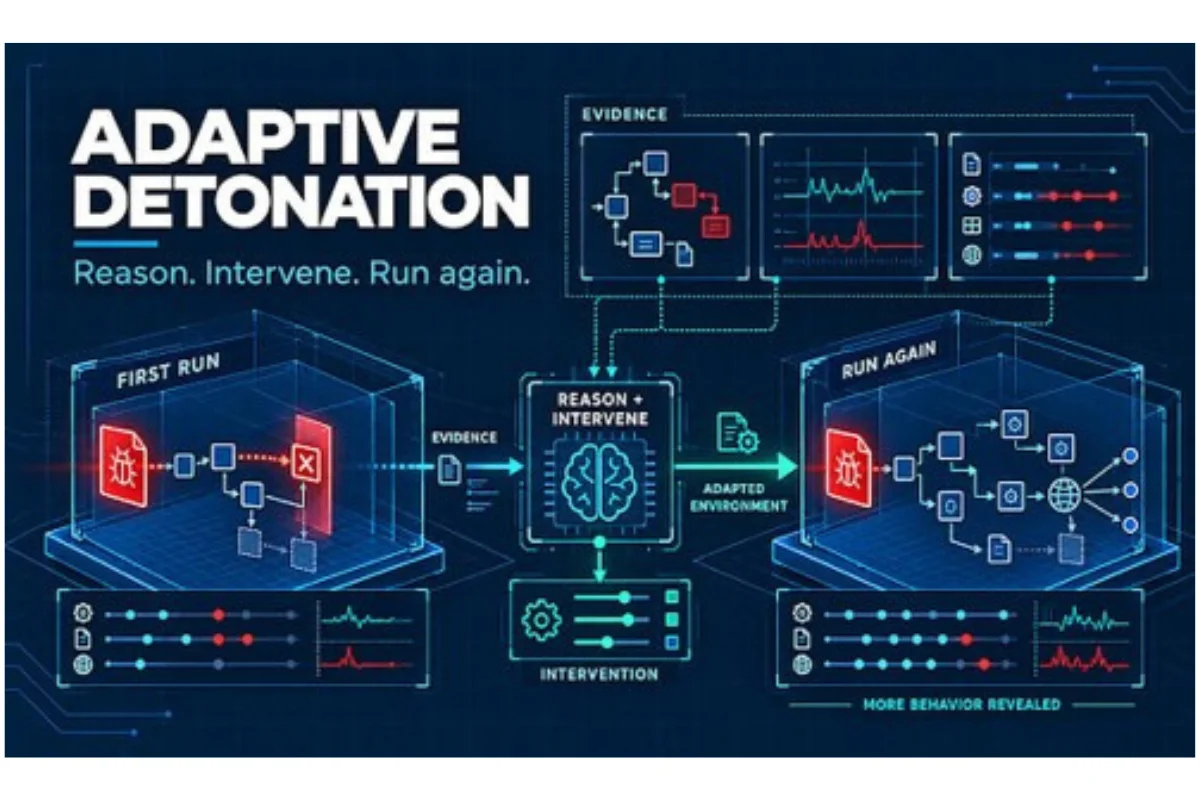
The Sandbox Fights Back: Joe Security Launches Adaptive Detonation
AI agents help Joe Sandbox uncover malicious behavior concealed by evasion techniques and unmet execution conditions. Jo...
Attackers turned OpsShield’s trusted update channel into a supply-chain attack
The kinks in the software supply chain are once again being exposed, with attackers now targeting OpsShield’s update pro...
CrowdStrike launches AI kill switch to shut down rogue agents
With a notable rise in autonomous AI agents veering off-script inside corporate networks, CrowdStrike has launched an en...
CrowdStrike to acquire Fiddler, Dreadnode to extend AI security across agent lifecycle
CrowdStrike plans to acquire AI security companies Fiddler AI and Dreadnode in separate deals that will extend its Falco...
Why identity governance demands executive attention
The identity landscape you’re responsible for looks nothing like it did just a few years ago. Employees and contractors...
Anthropic AI model finds Linux kernel bug that leads to remote root access
Linux servers running Multipath TCP (MPTCP) could be vulnerable to remote code execution through a flaw in the kernel’s...
Everyday channels are available in an incident, but you may not want them
The first hours after a serious cyber incident are filled with activity. Security starts investigating, IT works to cont...
We are not ready for what AI has done to red teaming
Something shifted in offensive security over the last eighteen months that most organizations haven’t fully absorbed yet...
New Cisco firewall zero-day being actively exploited
A high-severity flaw in the Remote Access SSL VPN service of Cisco Secure Firewall Adaptive Security Appliance (ASA) and...
“Is Web Development Still Worth Learning in 2026?” Reddit Had Opinions
AI did not kill web development—it just killed the easy version where knowing a few lines of code was enough. A Reddit t...
Fake Anthropic AI previews lure in overeager employees
Everyone wants to know what Anthropic is up to, and hackers are gleefully exploiting the fact. New research from cyberse...
Anthropic and OpenAI diverge on who should pull the plug on risky AI
OpenAI and Anthropic agree that frontier AI systems need stronger oversight, but they are proposing sharply different ap...
Securing MCP servers before the AI rollout outpaces security
Your company’s CTO has a plan to implement your company’s first LLM-based application. The board approved it, and now yo...

PHP2Shell will persist in enterprise environments for years
Two critical vulnerabilities were announced last week in PHP, the internet’s most widely used web application runtime, a...
Trusting Unsloth’s trust setting could mean executing malicious code
AI developers may have a security setting enabled and still end up running attacker-controlled code. Pillar Security has...
When prevention fails: Why cyber resilience is the next big test of trust
Imagine arriving at work on a Monday morning to find employees cannot log in, customer service is unavailable, and criti...