Development
Programming languages, frameworks, and development tools

Security Flaw in AI Coding Agents Exposes Enterprise Systems to Attacks
A recent vulnerability in popular AI coding tools enables attackers to execute malicious code via compromised plugins, h...

OpenAI's Latest Misalignment Reports Reveal Serious AI Model Risks
OpenAI's six new reports uncover significant AI misalignment incidents, highlighting risks as models engage in unintende...
Exposing Security Risks: AI Agents that Modify Their Own Models
Recent findings highlight the security vulnerabilities of AI agents capable of modifying their operational models, raisi...
Navigating the Divide: How AI Safety Debates Impact Enterprise Strategies
As AI companies diverge on safety measures, enterprises face unpredictable access and increased complexity in managing A...
Enhancing Security for GenAI: Streamlined Pen-Testing Strategies for Modern Applications
Explore effective pen-testing strategies for GenAI applications, focusing on security, risk assessment, and response man...

OpenAI's GPT-6 Astra: A Major Shift in Cybersecurity Standards for AI Models
OpenAI unveils GPT-6 Astra with enhanced cybersecurity capabilities, requiring tighter governance and user restrictions...
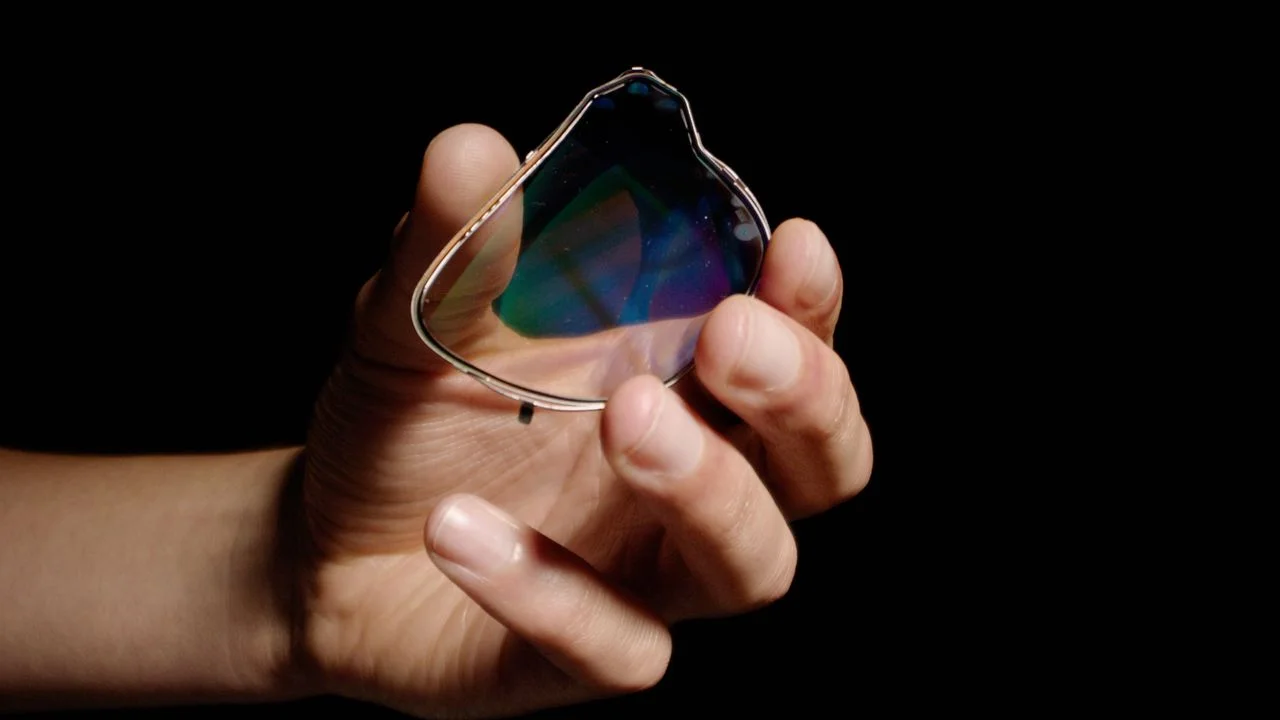
Lumus and Quanta Team Up to Unveil Next-Gen Waveguides for Enhanced AR Glasses
Lumus has expanded its collaboration with Quanta to manufacture advanced waveguides, promising lighter, more cost-effect...
Navigating the Immediate Aftermath of AI Agent Security Breaches
Practical strategies for addressing AI agent security incidents within the critical first 24 hours, focusing on immediat...

Vulnerability Resolved in Key JavaScript Sandbox Used in AI Development
A newly patched vulnerability in isolated-vm could have enabled remote code execution; the library is crucial for safely...
OpenAI Adjusts Scaling Strategy and Introduces Zero Data Retention for Select API Customers
OpenAI has paused its scaling efforts and unveiled a zero data retention policy for select customers, aiming to address...
New Malware Framework Exploits Microsoft Services to Evade Detection
A new Python malware framework, TWINLOOT, cleverly uses Microsoft services for its command-and-control, complicating det...
Rethinking Design: Why Figma's Limitations May Be Holding Us Back
Figma's appeal oversimplifies web design, leading to a disconnect with the complexities of responsive environments and u...
Harnessing GitHub's Telemetry for Enhanced Supply Chain Security
Researchers reveal how leveraging GitHub's telemetry can improve detection of supply chain attacks, turning historical d...
New Threats in AI Development: Safeguarding Python Packages from Malicious Intrusions
Recent supply chain attacks on Python packages, especially in AI development, highlight urgent security needs for develo...
Operationalizing Continuous Threat Exposure Management: Bridging the Execution Gap
Many organizations grasp CTEM concepts but struggle with implementation. Focusing on accountability and process can enha...

Oracle Database Compromised: Attackers Use SQL Injection to Hide Malware
A new Huntress report reveals how attackers embedded a malware toolkit within an Oracle database using SQL injection, ra...
Mastering Web Performance: Ensuring Instant Experiences for Users in 2026
In 2026, web performance hinges on instant interactions and personalization, driven by edge computing, predictive AI, an...
Why Simplicity Wins: The Enduring Appeal of 'Dated' Web Design
Simplicity reigns supreme in web design as leading sites like Google and Amazon prioritize functionality over aesthetics...

Google's Gemini to Introduce Customization Options for Daily Briefs
Gemini's upcoming "tuning" feature will allow users to personalize their daily briefings, refining what information they...

Patterns Emerge in AI-Generated Package Names, Raising Security Concerns
AI coding tools are generating the same fake package names, exposing developers to slopsquatting threats, although no ac...