Security teams often grapple with an overload of data rather than a deficit, leading to confusion instead of clarity. In this context, a global investment firm with operations in 18 locations faced a pivotal challenge: among countless findings from vulnerability scanners and penetration tests, how could they determine which risks truly mattered? The sheer volume of data often paralyzed decision-making, making it even more critical for the team to sift through every report and extract actionable insights.
The firm's small security engineering team faced the daunting task of navigating a complex environment while managing various projects, including infrastructure management and identity oversight. With data pouring in, their struggle wasn't merely to identify issues; it was to understand which ones posed real threats and how to prevent leadership from facing surprises due to overlooked vulnerabilities. This isn't just a technical hurdle; it’s a matter of trust and accountability. When leadership is blindsided by security issues, it can damage reputations and lead to costly consequences.
Implementing Continuous Validation
Recognizing the limits of traditional, point-in-time testing methods, the firm transitioned to a continuous validation strategy. This progressive approach allowed them to regularly reassess and validate their risk landscape without overwhelming their already lean team. Continuous validation isn't just a buzzword; it reflects a shift in mindset towards an ongoing security posture. The results were remarkable: impacts from internal penetration tests dropped from 251 to zero, as did compromised credentials and hosts. Additionally, cracked Active Directory passwords also fell to zero, showcasing their newfound, proactive stance in addressing vulnerabilities before they could be exploited.
The Impact of Identified Weaknesses
While expecting some lingering weaknesses, the team was astounded by the interconnected nature of vulnerabilities that could result in severe security breaches. For instance, an early internal pentest highlighted 85 vulnerabilities, but it was the combination of these weaknesses that led to a staggering 251 possible impacts, such as domain and host compromises, as well as data exposure. The realization that a single vulnerability could open the door to multiple threats underscored the importance of holistic security efforts.
The NodeZero® software illustrated these potential risks in a concrete manner. As one team member aptly stated, “That impact section in NodeZero is just pure evidence of what can happen in a real-life scenario.” This tangible representation transformed their discussions from merely cataloging weaknesses to understanding their broader implications for business impact. Data is not enough; understanding what that data means and how it translates into real-world risks is where the real challenge lies.
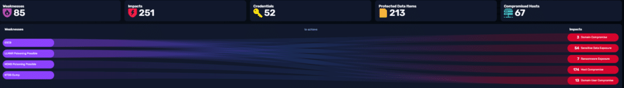 Figure 1. An early internal pentest identified 85 vulnerabilities leading to 251 potential security impacts.
Background of the Transition
This investment firm was already investing significant resources into security oversight, yet the requirement wasn’t simply about adding another tool; it was about establishing a scalable approach that wouldn’t encumber a small team juggling multiple responsibilities. As the senior security engineer noted, “NodeZero is, let’s say, 5% of my work. I’m dealing with a million different things, a million different projects, a million different responsibilities.” This reflects a reality many security teams face: balancing priorities against limited personnel and time. Operational simplicity became essential amidst competing demands, with clarity around security processes increasingly becoming a top priority.
Prior experience with security platforms that demanded significant infrastructure upkeep had taught the team the importance of minimizing overhead. NodeZero delivered a straightforward deployment and operational paradigm, enabling immediate testing without the burden of complex infrastructure. The firm sought not just a temporary proof of concept but a sustainable program capable of evolving alongside their business. Any new system adopted had to complement their workflows, not complicate them.
(And this is the part most people overlook) The decision to pursue continuous validation was not merely operational; it represented a cultural shift within the organization towards embracing proactive rather than reactive security management. Security no longer had to be a hurdle but instead became an integrated part of the firm's operational ethos.
Click here for a deeper look into the challenges faced by the organization and their mitigation strategies.
Focusing on Validating Outcomes
The ambition was never about eradicating each vulnerability; it was about clarifying the uncertainties tied to the most pertinent risks. This shift from merely measuring activities to validating tangible outcomes encapsulates the firm’s new philosophy. They learned that the quantity of tests or findings didn’t equate to effectiveness.
Instead, understanding the impact of those vulnerabilities became the objective. If you're working in this space, you know that it’s all too easy to get lost in metrics without grasping their implications. An effective security program isn’t just about numbers; it’s about translating those numbers into risk management tactics that allow for informed decision-making.
To further explore Horizon3.ai and NodeZero, click here.
Future Outlook
The firm’s experience may reflect a larger trend in cybersecurity strategy among organizations facing similar challenges. As security threats evolve and become more sophisticated, companies are likely to embrace continuous validation more widely. Expect vendors to respond with more advanced solutions that integrate real-time risk assessment and analysis, making security both proactive and predictive.
In the years ahead, organizations adopting such strategies will need to focus not only on tools but also on fostering a culture of accountability and awareness. Security won't just be the responsibility of a few; it must become everyone’s priority. The path to effective cybersecurity involves collaboration, education, and an unyielding commitment to understanding and managing risks in a very real and actionable manner.


